Certification track: AI Tooling
OpenClaw on GKE Autopilot
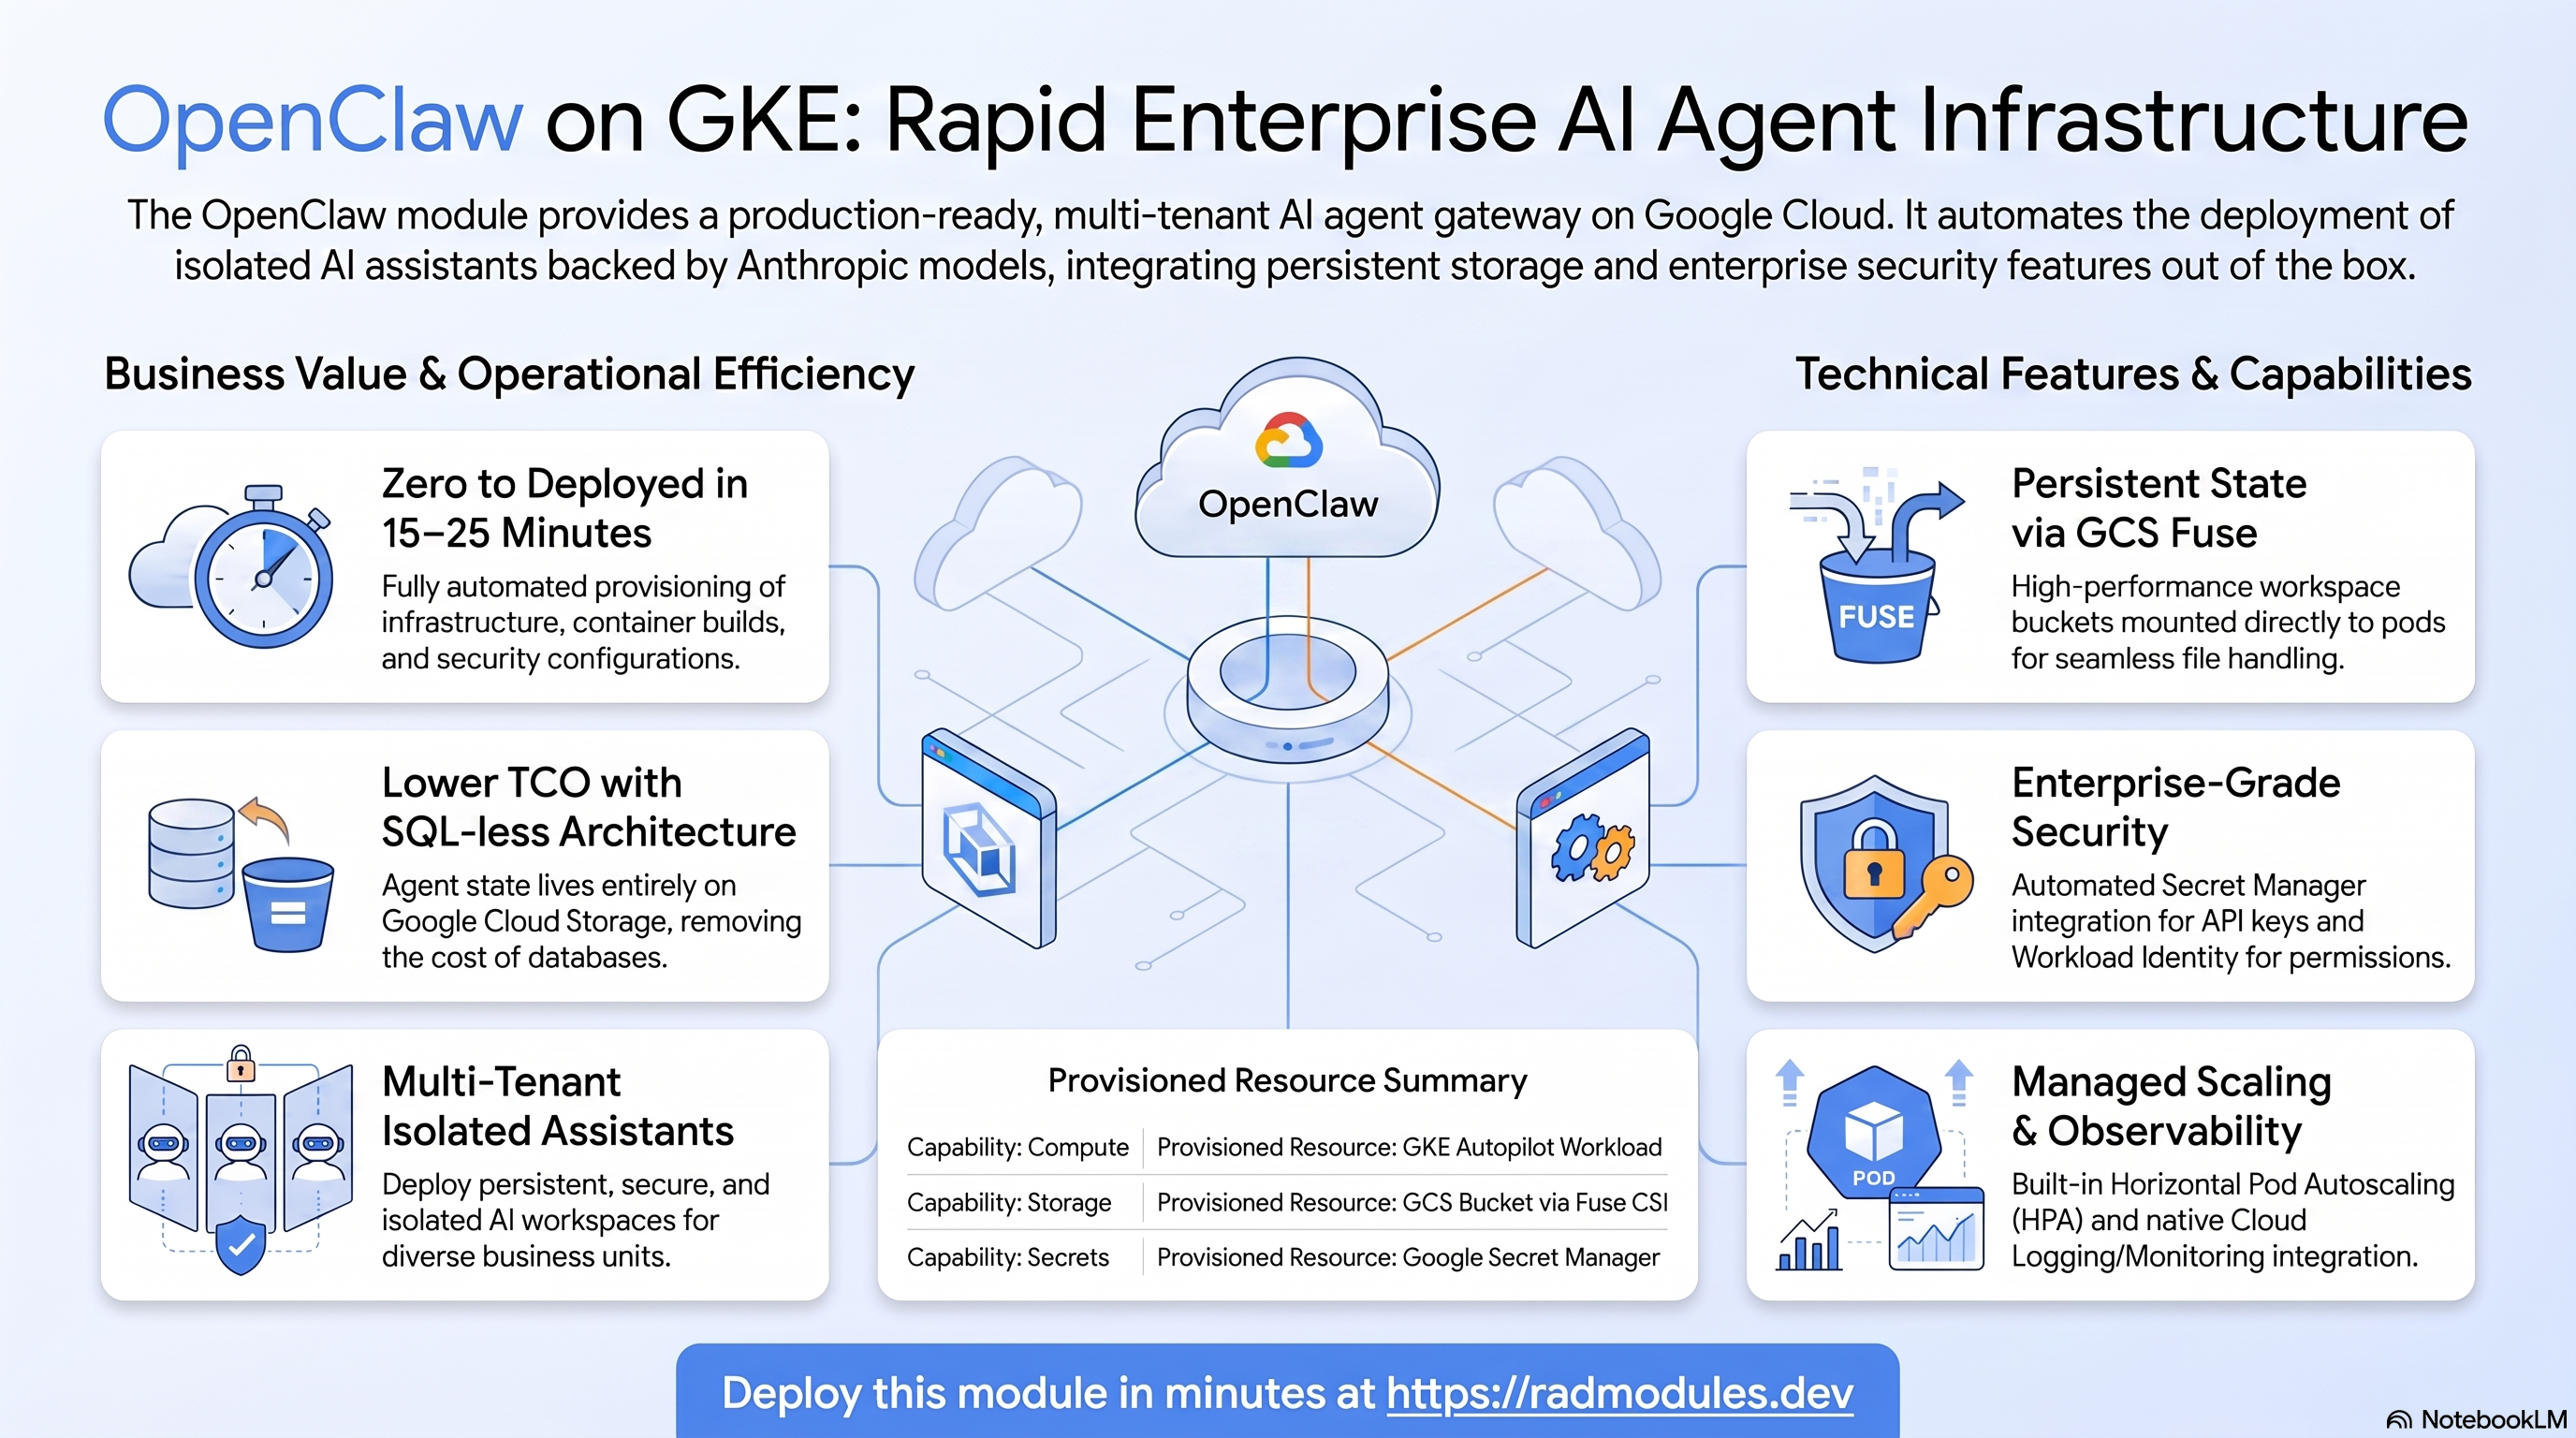
OpenClaw is a multi-tenant AI agent gateway purpose-built for isolated, persistent agent deployments. It lets teams run per-tenant AI assistants backed by Anthropic models, with dedicated GCS workspaces and optional Telegram or Slack channel integration — all without shared state between agents. This module deploys OpenClaw on GKE Autopilot on top of the App_GKE foundation, which provisions and manages the shared Google Cloud and Kubernetes infrastructure.
This guide focuses on the cloud services OpenClaw uses and how to explore and operate them from the Google Cloud Console and the command line. For the mechanics common to every GKE application — Workload Identity, ingress, autoscaling, CI/CD, Cloud Armor, IAP, Binary Authorization, VPC Service Controls, backups, and the deployment lifecycle — refer to the App_GKE foundation guide rather than repeating them here.
What OpenClaw costs on RAD, and how that compares
OpenClaw on RAD's GKE Autopilot module costs about US$129–202 a month, with the module fee charged once in RAD credits. GKE Autopilot suits OpenClaw that must stay up, scale across pods or run beside other Kubernetes workloads; for the lowest cost, the Cloud Run module runs the same OpenClaw for about US$69 a month. If you only need it occasionally — a demo, a seasonal project, something you're evaluating — a RAD-managed project can be deleted and restored within 30 days for a handful of credits (under US$1) instead of paying for it to sit idle. See Pause it for free, below. Figures are as at 8 October 2026; sources are listed at the end of this section.
What you pay on RAD
RAD deploys OpenClaw, which is open source, so there is no licence fee per user. You pay for three things:
| In a Google Cloud project you own | In a project RAD manages for you | |
|---|---|---|
| Module fee, once per deployment | 110 credits (US$11 at the top-up price) | 99 credits (10% lower) |
| Build time | About 3-6 credits per build | The same |
| Google Cloud running cost | Billed by Google to your own billing account, about US$129 a month for the default configuration (table below) — more if this isn't your only Autopilot cluster | Metered hourly in credits; RAD publishes 105 credits a day, about 3,150 a month (about US$315 at the top-up price, US$252 at the Scale plan's rate) |
| Who owns what | You own the project and its billing; RAD deploys and updates it | RAD owns the project, with guardrails, quotas and budget alerts; you get console access, and a minimum purchased balance is held in reserve |
10 credits cost US$1 on a one-off top-up, and less on a monthly plan. In a project RAD manages, the database, file server and network are shared by every application in the project, so a second application does not add a second set of them.
Default running cost in your own project (us-central1, Google list prices):
| Resource (module default) | Per month |
|---|---|
| GKE Autopilot pod, 2x vCPU / 2 GiB | US$72.16 |
| Cloud SQL for PostgreSQL, 1 vCPU / 3.75 GB, zonal, 10 GB SSD | US$51.02 |
| Cloud NAT and networking | US$5 |
| Cloud Storage (add-ons, backups) | US$1 |
| GKE cluster management fee | shared across every GKE app in the project; $0 if this is your only cluster, else ~73 |
| Total | about US$129 (about US$202 if this isn't your only Autopilot cluster) |
How it compares
- No turnkey managed SaaS was verified for OpenClaw itself, so the honest comparison is a self-managed server: a Hetzner CPX22 (2 vCPU/4 GB) costs about $24/month, a DigitalOcean 2 vCPU/4 GB Droplet about $24/month, and a GCP Compute Engine e2-standard-2 (2 vCPU/8 GB) about $49/month.
- This is a light workload — a cheaper, smaller VPS class than the reference boxes below would also do the job; the figures are shown for a like-for-like comparison.
- OpenClaw is a bespoke multi-tenant AI agent gateway with no off-the-shelf SaaS equivalent to compare against. The realistic alternative is building the same per-tenant isolation (separate workspaces, secrets, channel integrations) yourself on a VPS or managed Kubernetes, which is materially more engineering effort than RAD's one-click deploy, on top of needing your own managed PostgreSQL.
- The VPS price is not the whole cost. On a bare VPS you are also the one patching the OS, rotating backups and keeping the database (if any) healthy. RAD's managed Cloud SQL, Secret Manager and monitoring cover that for you, which is the real argument for RAD over a cheaper box — not the sticker price.
Pause it for free: delete a RAD-managed project, restore it when you need it
If OpenClaw runs in a project RAD manages for you, you have a second option that goes well beyond scaling to zero: delete the whole project, and restore it within 30 days for close to nothing. This suits OpenClaw you only need occasionally — a demo, an evaluation, a seasonal project — far better than running it continuously.
- How it works. Deleting a RAD-managed project unlinks its billing first, then asks Google to delete the project. Google does not remove the project immediately: it keeps it, recoverable, for 30 days. Because billing is already unlinked, nothing is charged while it waits. Unlike deleting one module, this does not tear down the database, the cluster or the compute resource one by one — the whole project, and everything in it, simply stops.
- Restoring costs a few credits, not a rebuild. Within 30 days, the project's owner can restore it. RAD asks Google to undelete the project and reattaches its billing account, then asks you to run Update on each deployment to confirm everything came back. Because nothing was individually destroyed, that Update finds the same resources already there — it is a check, not a rebuild, and an Update never charges the module fee again. That costs roughly a handful of credits (under US$1) in total for a typical 2-3-deployment chain.
- So a month of occasional use can cost a few dollars, not US$129. Deploy OpenClaw, use it for a while, delete the project. Restore it next time you want it, confirm with Update, and delete it again when you're done. You pay only for the module fee once, the builds, and whatever time OpenClaw was actually live.
- What this needs. You must own the project (not a bring-your-own one RAD only manages billing for), and you restore it yourself within the 30 days — after that, Google deletes it for good. Restoring is admitted like creating a new project: your purchased credit balance must still clear the tier's floor (100 credits for the sandbox tier most study and demo use fits). Google says most services are fully working again within 36 hours of a restore.
- One real gap: nightly backups don't survive. Backups are written to a bucket inside the project, and that bucket is not protected by Cloud Storage's soft-delete, so it is very likely gone as soon as you delete the project — even though the project itself is recoverable for 30 days. If you've customised OpenClaw and want to keep that work, copy a backup out (to Google Drive, or a bucket outside the project) before you delete. For a default installation with nothing irreplaceable in it, this does not matter.
Pay only while you use it, the other way: delete and redeploy
The option above only applies to a RAD-managed project; in your own project, or once the 30-day window has passed, the way to stop paying is to delete the deployment and deploy it again when you need it.
- What a redeploy costs. The module fee again plus the builds: about 115 credits (US$11.50) in your own project, or 104 credits in a RAD-managed one. Deleting saves money once OpenClaw would otherwise sit unused for about 3 days or more in your own project (about US$4.31 a day), or about 1 days or more in a RAD-managed one (105 credits a day).
- Most of the running cost is usually the database and any shared file/cache VM. They stop only when nothing else in the project uses them, so deleting OpenClaw while something else shares the project saves only this app's own compute part.
- Keep your data first. Nightly backups go to a bucket inside the deployment and are deleted with it, so copy the latest backup out before deleting if you want to keep it.
Lab sessions and Managed Environments
- Lab sessions, for training. A trainer runs a session for a class. Each participant gets OpenClaw in their own Google Cloud project for 15 minutes to 24 hours, within an allowance the trainer sets. Either the trainer funds every place, or each participant pays for their own. Everything is deleted when the session ends and unused credits go back to the trainer.
- Managed Environments, for consultancies. A partner runs OpenClaw for a client from a ring-fenced wallet it funds, and settles with the client directly. If the wallet runs low, billing pauses and the data is kept, so nobody receives an unexpected charge. At the end the partner hands the project over and the deployments become the client's own.
- Credits can be bought in more than 20 currencies, including XAF, XOF, NGN, GHS, KES and ZAR, by card, bank transfer or mobile money.
Sources (8 October 2026): Google Cloud list prices from the Cloud Billing Catalog API; Delete and restore projects for the 30-day recovery window and what it says about Cloud Storage objects without soft delete; RAD fees and the daily-credit estimates from radmodules.dev/pricing. Prices change; check each source before relying on a figure.
1. Overview
OpenClaw runs as a Node.js gateway workload on GKE Autopilot. The deployment wires together a focused set of Google Cloud services:
| Capability | Google Cloud service | Notes |
|---|---|---|
| Compute | GKE Autopilot | Node.js pods, 2 vCPU / 2 GiB by default, horizontally autoscaled |
| Workspace storage | Cloud Storage (GCS Fuse) | Per-tenant workspace bucket mounted at /data via the GCS Fuse CSI driver |
| AI credentials | Secret Manager | Anthropic API key and gateway token always stored; Telegram and Slack secrets optional |
| Ingress | Cloud Load Balancing | LoadBalancer by default (public external IP); ClusterIP or a custom domain available |
| Secrets | Secret Manager | All credentials injected at pod startup; plaintext never in config |
Sensible defaults worth knowing up front:
- No database, no Redis. OpenClaw is a stateful Node.js gateway backed entirely by GCS
Fuse at
/data. Cloud SQL and Redis are never provisioned. - Custom container image is always built. The module layers an
entrypoint.shonto the upstreamghcr.io/openclaw/openclawimage. TheBASE_IMAGEbuild arg is pinned toapplication_version. - GCS workspace at
/datais always mounted. A dedicated<prefix>-storagebucket is always provisioned and mounted by the GCS Fuse CSI driver. Persistent agent state lives here across pod restarts. OPENCLAW_STATE_DIRis on local disk. npm staging and the XDG config home are redirected to/tmp/openclawto avoid GCS Fuse hard-link limitations during startup.min_instance_count = 1by default. Keeps the agent warm so webhook events from Telegram or Slack are not dropped during cold-start.- Session affinity is
ClientIP. Ensures a user's WebSocket sessions are consistently routed to the same pod when more than one replica is running.
2. Google Cloud Services & How to Explore Them
All commands assume you have run
gcloud container clusters get-credentials <cluster> --region <region> --project <project>
and that PROJECT, REGION, and NAMESPACE are set. The namespace and other identifiers
are reported in the deployment Outputs.
A. GKE Autopilot — the OpenClaw workload
OpenClaw pods are scheduled on Autopilot, which bills for the CPU/memory the pods actually request. Horizontal Pod Autoscaling sizes the deployment between the minimum and maximum replica counts.
- Console: Kubernetes Engine → Workloads → select the OpenClaw workload to see pods, events, and resource usage. Kubernetes Engine → Services & Ingress shows the service endpoint.
- CLI:
kubectl get pods,svc,hpa -n "$NAMESPACE"
kubectl logs -n "$NAMESPACE" deploy/<service-name> --tail=100
kubectl describe hpa -n "$NAMESPACE"          # current vs target utilisation
See App_GKE for how Autopilot, scaling, and the workload type (Deployment vs StatefulSet) are managed.
B. Cloud Storage — GCS Fuse workspace
All durable agent state is stored in a dedicated Cloud Storage bucket and mounted into pods
at /data by the GCS Fuse CSI driver. The workspace layout is:
<prefix>-storage/
├── workspace/              ← agent workspace (/data/workspace)
│   └── skill-library/      ← shared skills repo (when skills_repo_url is set)
├── agents/main/agent/      ← agent state directory
└── ...
- Console: Cloud Storage → Buckets → select the
<prefix>-storagebucket. - CLI:
gcloud storage buckets list --project "$PROJECT"
gcloud storage ls gs://<prefix>-storage/
# Confirm the bucket is mounted inside a pod:
kubectl exec -n "$NAMESPACE" deploy/<service-name> -- ls /data
See App_GKE for GCS Fuse CSI, CMEK options, and bucket lifecycle.
C. Secret Manager — credentials
The Anthropic API key and the gateway token are always stored in Secret Manager. When Telegram or Slack integration is enabled, the bot tokens and webhook/signing secrets are stored there as well. All credentials are injected at pod startup; plaintext never appears in configuration.
- Console: Security → Secret Manager.
- CLI:
gcloud secrets list --project "$PROJECT"
# Retrieve the Anthropic key (initial deploy only; manage via Secret Manager thereafter):
gcloud secrets versions access latest --secret=<prefix>-anthropic-api-key --project "$PROJECT"
# Retrieve the gateway token (needed to register clients):
gcloud secrets versions access latest --secret=<prefix>-gateway-token --project "$PROJECT"
See App_GKE for the Secret Store CSI integration and rotation.
D. Networking & ingress
By default the workload is exposed as a LoadBalancer service with a public external IP.
Set service_type = "ClusterIP" for internal-only access (typically behind an OpenClaw
router service), or enable a custom domain via the Kubernetes Gateway API for direct
external access on a stable hostname.
- Console: Kubernetes Engine → Services & Ingress; VPC network → IP addresses.
- CLI:
kubectl get svc,ingress -n "$NAMESPACE"
gcloud compute addresses list --project "$PROJECT"
See App_GKE for custom domains, Cloud Armor, and static IP details.
E. Cloud Logging & Monitoring
Pod stdout/stderr flow to Cloud Logging; GKE metrics flow to Cloud Monitoring. An optional uptime check and alert policies are available.
- Console: Logging → Logs Explorer; Monitoring → Dashboards / Alerting.
- CLI:
gcloud logging read 'resource.type="k8s_container" AND resource.labels.namespace_name="'"$NAMESPACE"'"' \
  --project "$PROJECT" --limit 50
3. OpenClaw Application Behaviour
- No database setup job. OpenClaw requires no Cloud SQL and no init job. The agent state
lives entirely on GCS; the first pod startup creates the workspace directories automatically
via
entrypoint.sh. - Config regenerated on every startup.
entrypoint.shalways rewritesopenclaw.jsonin$OPENCLAW_STATE_DIR, ensuring the Terraform-managed environment variables (API keys, gateway token, channel settings) win over any stale values previously persisted on GCS. - Skills repository sync (optional). When
skills_repo_urlis set,entrypoint.shperforms a shallow clone or update of the repository into/data/workspace/skill-libraryon every pod startup. The sync is non-fatal — the gateway starts even if the clone fails. Inspect the sync on a running pod:kubectl exec -n "$NAMESPACE" deploy/<service-name> -- ls /data/workspace/skill-library - Health path. Startup and liveness probes both target
GET /healthon port 8080. The startup probe allows up to ~3 minutes (36 × 5 s) for npm to stage the bundled plugin packages before the gateway is declared unhealthy. - Session affinity. The Kubernetes Service uses
ClientIPaffinity by default so a user's WebSocket connection is consistently routed to the same pod when multiple replicas are deployed. - Telegram and Slack. When
enable_telegramis set, the bot token is injected asTELEGRAM_BOT_TOKEN. Whenenable_slackis set, the bot token and the app-level token are injected asSLACK_BOT_TOKENandSLACK_APP_TOKEN, and the entrypoint connects the agent to Slack over Socket Mode: an outbound WebSocket that needs no public ingress and no router. Slack ships as the separate@openclaw/slackplugin, which the entrypoint installs on each boot. Access is fail-closed: DMs only from the member IDs inSLACK_ALLOW_FROM, channels only from the IDs inSLACK_CHANNELS(mention-gated), both passed throughenvironment_variables. The Telegram webhook secret and the optional Slack signing secret are stored in Secret Manager for a companion router service and are not injected into the agent container.
4. Configuration Variables
Variables are grouped exactly as they appear on the deployment platform. Only settings specific to or notable for OpenClaw are listed; every other input is inherited from App_GKE with its standard behaviour and defaults.
Group 1 — Project & Identity
| Variable | Default | Description |
|---|---|---|
project_id | (required) | Target Google Cloud project. |
region | us-central1 | Region for the workload and regional resources. |
anthropic_api_key | (required on first deploy) | Anthropic API key. Stored in Secret Manager and injected as ANTHROPIC_API_KEY. Omit on updates to retain the stored value. Sensitive. |
gateway_token | (auto-generated) | Gateway authentication token. A secure 64-character hex token is generated when left blank. Stored in Secret Manager as OPENCLAW_GATEWAY_TOKEN. Sensitive. |
Group 2 — Deployment Environment
| Variable | Default | Description |
|---|---|---|
tenant_id | demo | Short suffix that makes resource names unique per environment. |
support_users | [] | Emails granted project access and monitoring alerts. |
resource_labels | {} | Labels applied to all resources for cost/ownership tracking. |
Group 3 — Application Identity
| Variable | Default | Description |
|---|---|---|
application_name | openclaw | Base name for resources. Do not change after first deploy. |
application_display_name | OpenClaw Gateway | Friendly name shown in the Console. |
description | OpenClaw AI Gateway - Multi-tenant AI agent gateway on GKE Autopilot | Brief description of the application's purpose. |
application_version | latest | OpenClaw image tag used as the BASE_IMAGE build arg. Pin to a specific release for reproducible builds. |
Group 4 — Runtime & Scaling
| Variable | Default | Description |
|---|---|---|
deploy_application | true | Set false to provision infrastructure only. |
container_resources | { cpu_limit = "2000m", memory_limit = "2Gi" } | CPU and memory limits. Minimum 2 vCPU / 2 GiB recommended for agent workloads. |
min_instance_count | 1 | Minimum pod replicas. Keep ≥ 1 so webhook events are not dropped during cold start. |
max_instance_count | 3 | Maximum pod replicas. OpenClaw is stateful — use 1 per tenant unless using sticky session routing. |
container_port | 8080 | Port the OpenClaw gateway listens on. Must match the PORT env var. |
timeout_seconds | 3600 | Request timeout. Agent sessions are long-running; 3600 s is the maximum. |
enable_image_mirroring | true | Mirror the built image to Artifact Registry before deployment. |
enable_vertical_pod_autoscaling | false | Let Autopilot tune resource requests automatically (disables HPA). |
Group 5 — Environment Variables & Secrets
| Variable | Default | Description |
|---|---|---|
environment_variables | {} | Extra non-secret settings. Module-managed vars (OPENCLAW_STATE_DIR, NODE_ENV, etc.) always take precedence. |
secret_environment_variables | {} | Map of env var → existing Secret Manager secret name. Core credentials are handled automatically. |
secret_propagation_delay | 30 | Seconds to wait after secret creation before proceeding. |
Group 6 — GKE Backend & Cluster
| Variable | Default | Description |
|---|---|---|
gke_cluster_name | "" | GKE cluster name. Auto-discovers the Services_GCP-managed cluster when empty. |
namespace_name | "" | Kubernetes namespace. Auto-generated from resource prefix when empty. |
workload_type | null | Deployment for GCS-backed stateless replicas; StatefulSet for sticky pod identity. |
service_type | LoadBalancer | ClusterIP for internal-only; LoadBalancer for direct external access. |
session_affinity | ClientIP | Sticky routing for WebSocket session consistency across replicas. |
termination_grace_period_seconds | 60 | Grace period for active agent sessions to complete before pod termination. |
network_tags | [] | Node/pod network tags for firewall rules. |
Group 7 — StatefulSet Configuration
| Variable | Default | Description |
|---|---|---|
stateful_pvc_enabled | null | Enable a PVC for StatefulSet. OpenClaw normally uses GCS — enable only when local disk performance is required. |
stateful_pvc_size | 10Gi | PVC size. |
stateful_pvc_mount_path | /pvc-data | Container mount path for the PVC. |
stateful_pvc_storage_class | standard-rwo | Kubernetes StorageClass for PVCs. |
stateful_headless_service | null | Create a headless Service for stable network identities. |
stateful_pod_management_policy | null | OrderedReady or Parallel. |
stateful_update_strategy | null | RollingUpdate or OnDelete. |
stateful_fs_group | 0 | fsGroup GID in the pod security context; 0 leaves it unset. |
Group 8 — Resource Quota
| Variable | Default | Description |
|---|---|---|
enable_resource_quota | false | Cap namespace CPU/memory/object counts. |
quota_memory_requests / quota_memory_limits | "" | Must use binary units (4Gi, 8192Mi) — bare integers are read as bytes and block scheduling. |
Group 9 — Reliability Policies
| Variable | Default | Description |
|---|---|---|
enable_pod_disruption_budget | true | Protect availability during node upgrades. |
pdb_min_available | 1 | Raise min_instance_count above 1 if you need eviction headroom. |
enable_topology_spread | false | Spread pods across zones. |
Group 10 — Observability & Health
| Variable | Default | Description |
|---|---|---|
startup_probe / startup_probe_config | HTTP /health, 36-attempt threshold | Allows ~3 minutes for npm startup and GCS Fuse mount. |
liveness_probe / health_check_config | HTTP /health | Restarts the pod if the gateway becomes unresponsive. |
uptime_check_config | { enabled = false } | Disabled by default for ClusterIP services (not externally reachable). |
alert_policies | [] | Optional metric alert policies. |
Group 11 — Workload Automation
| Variable | Default | Description |
|---|---|---|
initialization_jobs | [] | OpenClaw has no default init job. Use for custom workspace seeding. |
cron_jobs | [] | Recurring Kubernetes CronJobs (e.g. workspace archival). |
additional_services | [] | Sidecar or companion services (e.g. an OpenClaw router). |
Group 12 — CI/CD & GitHub Integration
Standard App_GKE Cloud Build / Cloud Deploy integration — see
App_GKE. Key inputs: enable_cicd_trigger,
github_repository_url, github_token, enable_cloud_deploy.
Group 13 — NFS
| Variable | Default | Description |
|---|---|---|
enable_nfs | false | OpenClaw uses GCS Fuse for state. NFS is not required and disabled by default. |
nfs_mount_path | /mnt/nfs | NFS mount path. Only used when enable_nfs = true. |
Group 14 — Cloud Storage & Artifact Registry
| Variable | Default | Description |
|---|---|---|
create_cloud_storage | true | Provision additional buckets defined in storage_buckets. The workspace bucket is always created. |
storage_buckets | [] | Additional GCS buckets beyond the auto-provisioned workspace bucket. |
gcs_volumes | [] | Additional GCS Fuse mounts. The openclaw-data volume at /data is always appended. |
manage_storage_kms_iam / enable_artifact_registry_cmek | false | CMEK options. |
max_images_to_retain / delete_untagged_images / image_retention_days | (set) | Artifact Registry cleanup policy. |
Group 15 — OpenClaw Configuration
| Variable | Default | Description |
|---|---|---|
skills_repo_url | "" | GitHub URL of a shared skills repository. Cloned into /data/workspace/skill-library on every pod startup. Leave empty to skip. |
skills_repo_ref | main | Git ref (branch, tag, or SHA) to check out. |
enable_telegram | false | Provision a Telegram bot token secret and inject TELEGRAM_BOT_TOKEN. Requires telegram_bot_token. |
telegram_bot_token | "" | Telegram bot token from @BotFather. Sensitive. |
telegram_webhook_secret | "" | Webhook validation secret for the router (not injected into the agent). Generate with openssl rand -hex 32. Sensitive. |
enable_slack | false | Connect the agent to Slack over Socket Mode (outbound WebSocket — no ingress or router). Provisions Slack secrets and injects SLACK_BOT_TOKEN + SLACK_APP_TOKEN. Requires slack_bot_token and slack_app_token. |
slack_bot_token | "" | Slack bot token (xoxb-...). Sensitive. |
slack_app_token | "" | Slack app-level token (xapp-..., scope connections:write) for Socket Mode. Sensitive. |
slack_signing_secret | "" | Optional. Slack signing secret for an HTTP Request-URL router only (not injected; Socket Mode does not use it). Sensitive. |
Group 17 — Backup & Maintenance
| Variable | Default | Description |
|---|---|---|
backup_schedule | 0 2 * * * | Cron for automated workspace backup (UTC). |
backup_retention_days | 7 | Retention days; raise for production/compliance. |
enable_backup_import / backup_source / backup_uri / backup_format | restore options | Import a workspace backup on deploy. backup_format defaults to tar. |
Group 19 — Custom Domain & Static IP
| Variable | Default | Description |
|---|---|---|
enable_custom_domain | true | Provision a Kubernetes Gateway with SSL for custom hostnames. Required for IAP. |
application_domains | [] | Custom hostnames to serve. |
reserve_static_ip | true | Stable external IP across redeploys. |
Group 20 — Identity-Aware Proxy (IAP)
| Variable | Default | Description |
|---|---|---|
enable_iap | false | Require Google sign-in in front of OpenClaw. Requires enable_custom_domain. |
iap_authorized_users / iap_authorized_groups | [] | Who may access. |
iap_oauth_client_id / iap_oauth_client_secret | "" | Required when IAP is enabled. Sensitive. |
iap_support_email | "" | Shown on the OAuth consent screen. |
Group 21 — Cloud Armor
| Variable | Default | Description |
|---|---|---|
enable_cloud_armor | false | Attach a Cloud Armor (WAF) policy to the Ingress backend. |
cloud_armor_policy_name | default-waf-policy | Policy name. |
enable_cdn | false | Enable Cloud CDN on the load balancer backend. |
Group 22 — VPC Service Controls & Audit Logging
| Variable | Default | Description |
|---|---|---|
enable_vpc_sc | false | Enforce a VPC-SC perimeter (requires organization_id). |
vpc_cidr_ranges / vpc_sc_dry_run / admin_ip_ranges | (set) | Access level CIDRs / dry-run mode / admin CIDRs. |
enable_audit_logging | false | Detailed Cloud Audit Logs. |
5. Outputs
These values are returned on a successful deployment and are the quickest way to locate and explore the running resources.
| Output | Description |
|---|---|
service_name | Kubernetes Service name. |
namespace | Namespace the workload runs in. |
service_cluster_ip | In-cluster ClusterIP. |
stage_service_cluster_ips | Map of ClusterIPs for stage-specific services (Cloud Deploy). |
service_external_ip | External LoadBalancer IP (when a static IP is reserved). |
service_url | URL to reach the OpenClaw gateway. |
storage_buckets | Created Cloud Storage buckets (including the workspace bucket). |
network_name / network_exists / regions | VPC network, presence, available regions. |
container_image / container_registry | Deployed image and Artifact Registry repo. |
monitoring_enabled / monitoring_notification_channels | Monitoring status and channels. |
deployment_id / tenant_id / resource_prefix | Naming identifiers. |
project_id / project_number | Project identifiers. |
initialization_jobs | Names of any custom init jobs. |
cron_jobs | Names of created CronJobs. |
statefulset_name | StatefulSet name (when workload_type = "StatefulSet"). |
cicd_enabled / cicd_configuration | CI/CD status and details. |
github_repository_url / github_repository_owner / github_repository_name | Connected GitHub repo. |
artifact_registry_repository / cloudbuild_trigger_name / cloudbuild_trigger_id | Registry and build trigger. |
kubernetes_ready | true when the cluster endpoint is available and all Kubernetes resources are deployed. false on the first apply of a new inline cluster — a second apply is required. |
6. Configuration Pitfalls & Sensible Defaults
Risk: Critical (data loss / outage / security) — High (service degraded) — Medium (cost or partial degradation) — Low (minor).
| Setting | Sensible value | Risk | Consequence if wrong |
|---|---|---|---|
anthropic_api_key | Set on first deploy | Critical | Without a valid key the agent starts but all AI requests fail with 401 errors. |
gateway_token consistency | Auto-generated or set once | Critical | Rotating the token in Secret Manager without restarting pods causes all client requests to be rejected until pods are recycled. |
quota_memory_requests / quota_memory_limits | binary units | Critical | Bare integers are bytes and block all pod scheduling. |
enable_backup_import | false unless restoring | Critical | Enabling without a valid backup_uri fails the import job. |
telegram_bot_token / slack_bot_token | set when integration enabled | High | Empty token causes all API calls to fail; messages are dropped. |
telegram_webhook_secret / slack_signing_secret | set when integration enabled | High | Empty value disables signature verification, allowing fake webhook injection. |
min_instance_count | 1 | High | 0 means webhook events from Telegram/Slack are dropped during cold start (typically 30–60 s for GKE pod init). |
skills_repo_url | reachable URL or empty | High | An unreachable URL causes the git clone to fail at startup, putting the pod in CrashLoopBackOff. |
skills_repo_ref | existing ref | High | A non-existent branch or tag causes the clone to fail at every startup. |
session_affinity | ClientIP | High | Without stickiness, multi-replica deployments split WebSocket state across pods. |
enable_iap | enable for admin-facing | Medium | The gateway is otherwise publicly reachable. Telegram/Slack webhook endpoints cannot authenticate with Google identity — ensure they are not behind IAP. |
stateful_pvc_enabled | false | Medium | OpenClaw uses GCS. PVCs add unused local disk and can block rescheduling. |
backup_retention_days | 7 (raise for prod) | Medium | Too short for compliance; an accidental bucket purge permanently loses agent state. |
pdb_min_available vs min_instance_count | leave headroom | Medium | 1/1 can stall node upgrades (single pod cannot be evicted). |
enable_vpc_sc without organization_id | set explicitly | Medium | VPC-SC is silently skipped, leaving credentials without perimeter protection. |
For the foundation behaviour referenced throughout — IAM and Workload Identity, autoscaling, ingress and certificates, CI/CD, Cloud Armor, IAP, Binary Authorization, VPC-SC, backups, and image mirroring — see App_GKE. OpenClaw-specific application configuration shared with the Cloud Run variant is described in OpenClaw_Common.
Related guides
- Hands-on lab: OpenClaw on GKE Autopilot — deploy it step by step, with the console screens and commands at each stage.
- OpenClaw on Google Cloud Run — the same application on Cloud Run, for when you need the other deployment target.
- OpenClaw Common — Shared Application Configuration — the configuration shared by both deployment targets.
Need RAD to do something it does not do yet? Request it on the roadmap, or vote on what is already there.