Certification track: Professional Cloud DevOps Engineer (PDE)
n8n on Google Cloud Run
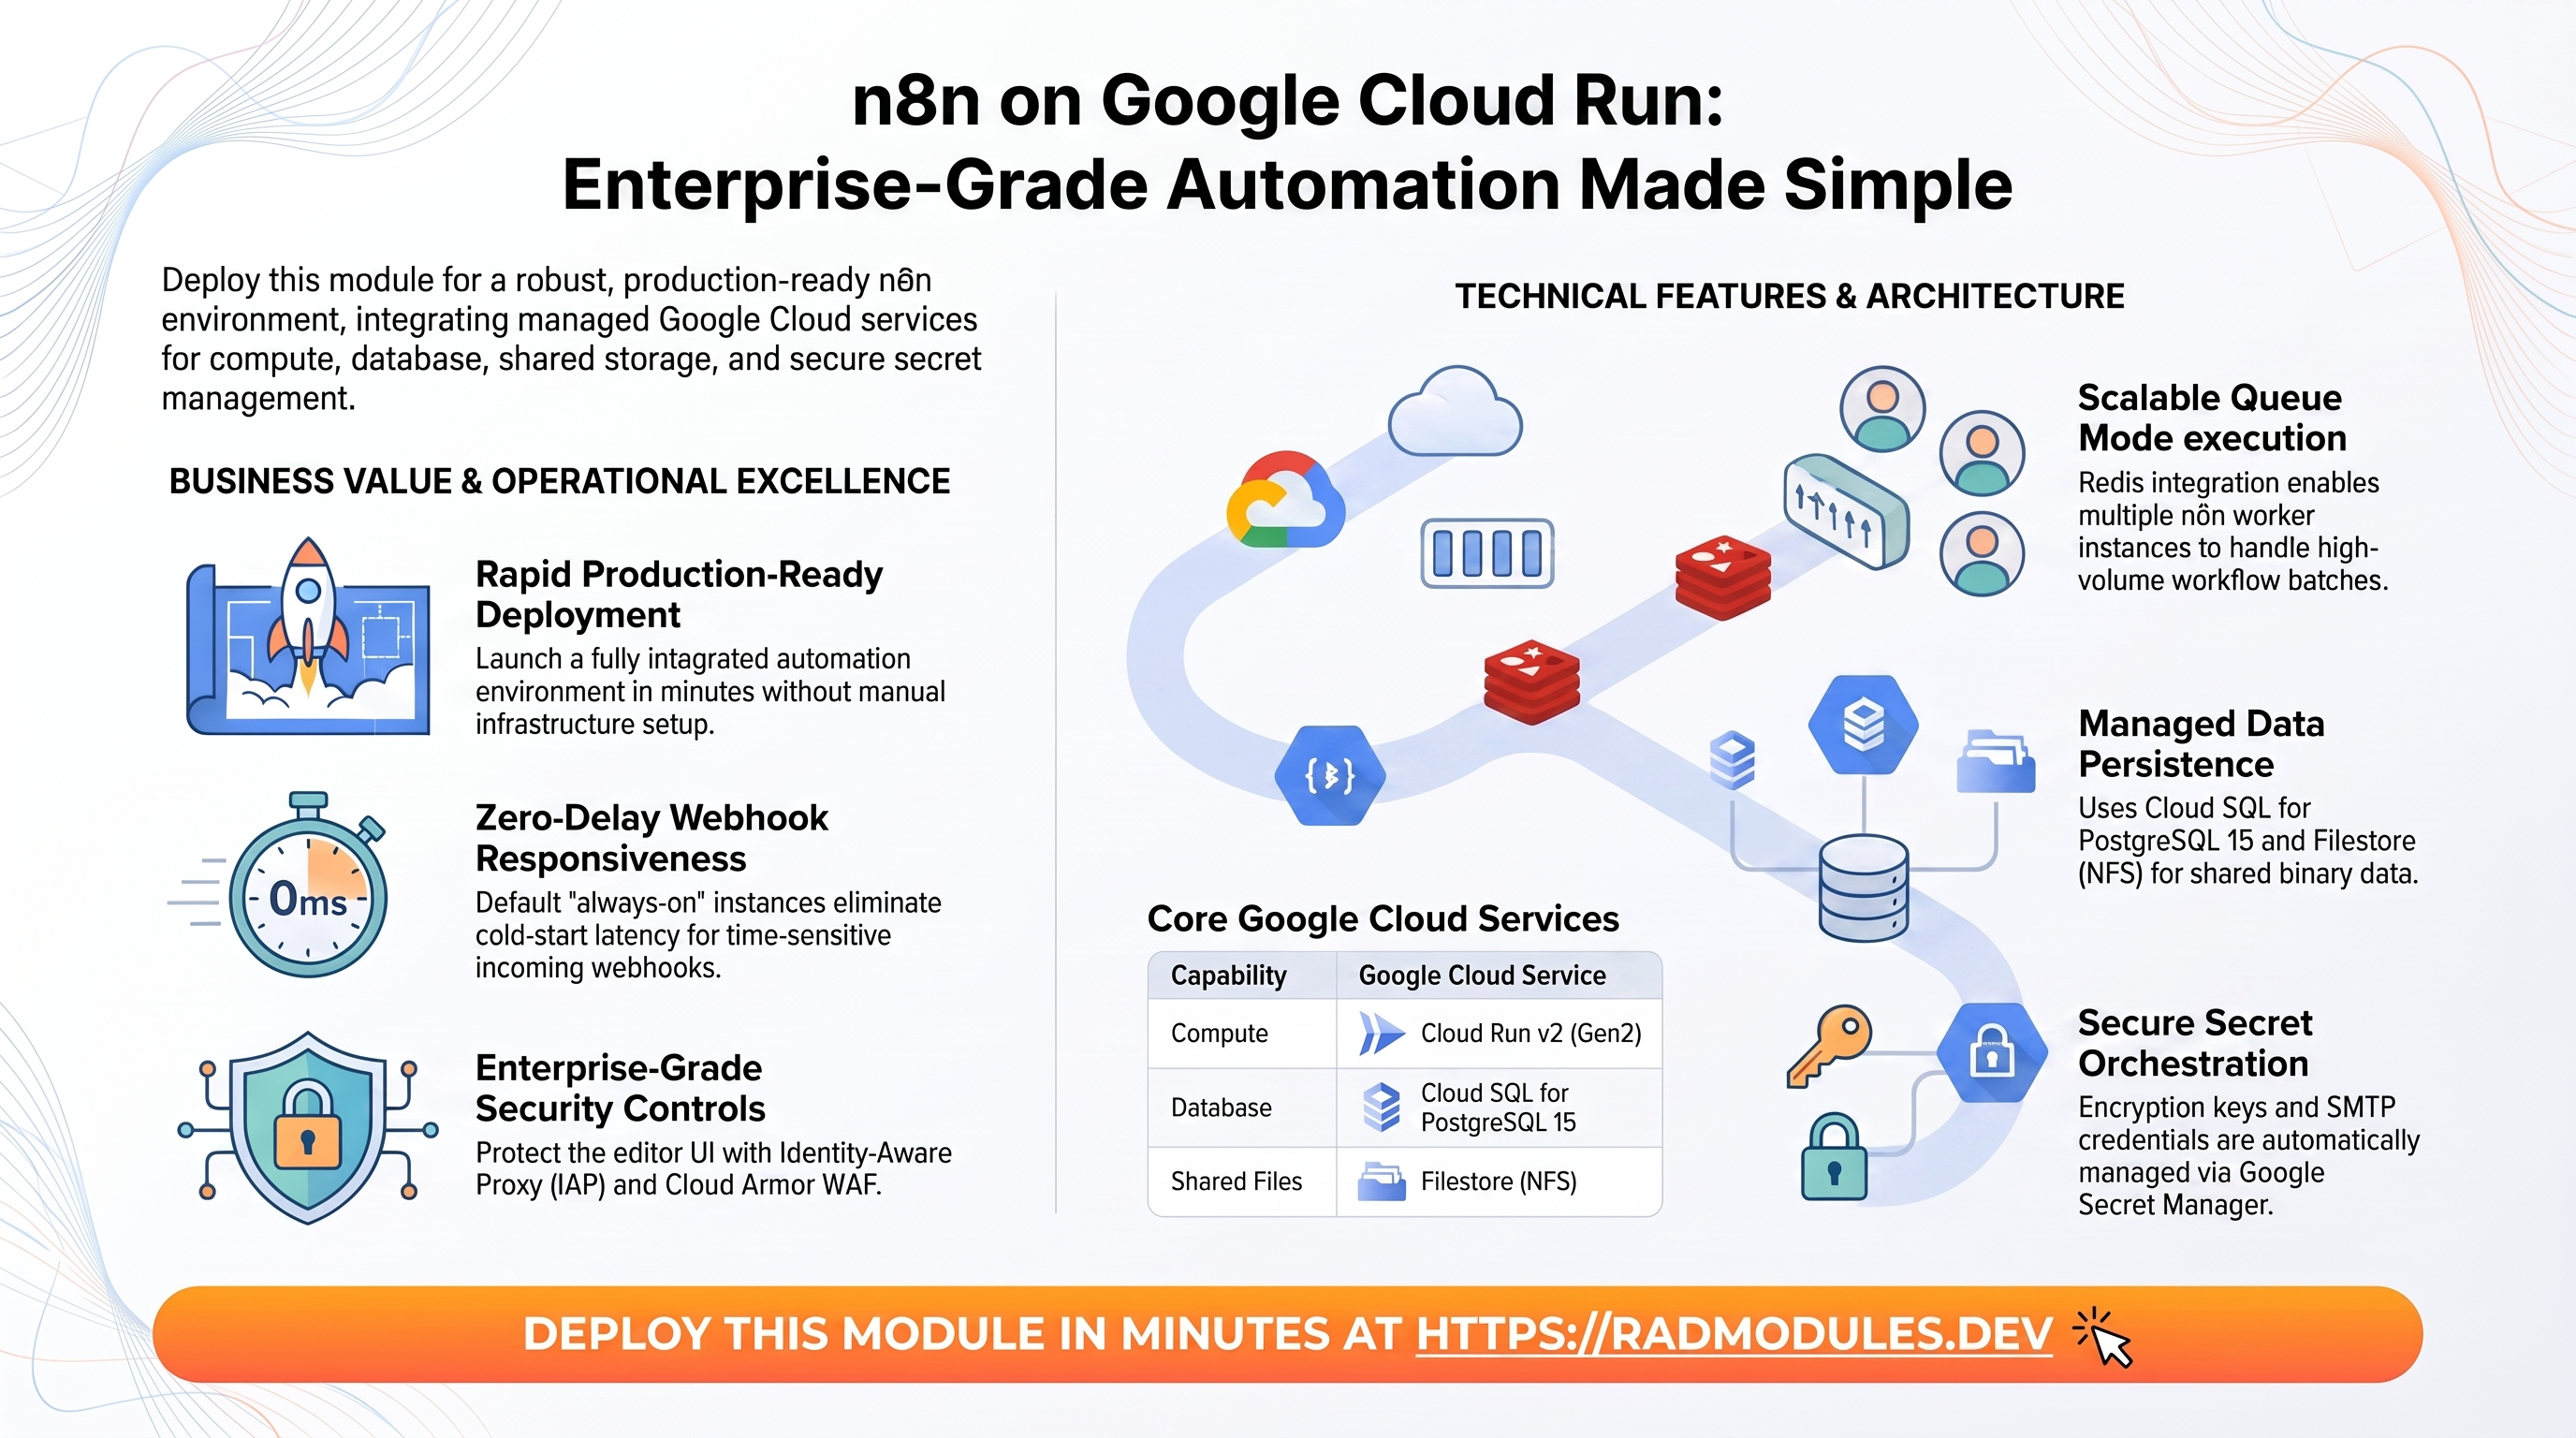
n8n is a fair-code workflow automation platform that connects APIs, databases, and services with a visual node editor. This module deploys n8n on Cloud Run v2 on top of the App_CloudRun foundation, which provisions and manages the shared Google Cloud infrastructure.
This guide focuses on the cloud services n8n uses and how to explore and operate them from the Google Cloud Console and the command line. For the mechanics common to every Cloud Run application — service identity, ingress and load balancing, scaling and concurrency, CI/CD, Cloud Armor, IAP, Binary Authorization, VPC Service Controls, backups, and the deployment lifecycle — refer to the App_CloudRun foundation guide rather than repeating them here.
What N8N costs on RAD, and how that compares
Running N8N in your own GCP project costs about $117.79/month in Google Cloud charges; RAD's module fee is a one-time 110 credits (or 99 credits in a RAD-managed project), covering setup and support -- not the ongoing cloud bill, which Google bills you directly in your own project or RAD meters hourly in credits in a RAD-managed one. Or see the GKE guide for the alternative deployment target; either way, if you deploy into a RAD-managed project you can pause the whole thing for free when you are not using it -- see Pause it for free below.
What you pay on RAD
| Your own project | RAD-managed project | |
|---|---|---|
| Module fee | 110 credits, once | 99 credits, once (10% lower) |
| Build time | metered in credits as the build runs (a few credits, typically) | same |
| Google Cloud running cost | ~$117.79/month, billed to your own billing account at Google's list price | ~55 credits/day, metered hourly by RAD at list price plus margin |
Default running cost in your own project
| Resource | US$/month (Google list price, us-central1) |
|---|---|
| Cloud Run, 1x vCPU / 1 GiB (alwaysOn) | $47.34 |
| Cloud SQL for PostgreSQL, 1 vCPU / 3.75 GB, zonal, 10 GB SSD | $51.02 |
| NFS/cache file server (small VM) | $13.43 |
| Cloud NAT and networking | $5.00 |
| Cloud Storage (add-ons, backups) | $1.00 |
| Total | $117.79 |
How it compares
- n8n's own official managed cloud (n8n Cloud) starts at €20/month billed annually for the Starter plan (2,500 workflow executions) (source: https://n8n.io/pricing), run by the project itself with no infrastructure to operate -- the comparison that matters here is less the sticker price and more whether you want the vendor's own cloud or your own GCP project with RAD managing it.
- Running it yourself on a bare VPS sized to this workload (a smaller box is enough -- Hetzner CX11-class or a DigitalOcean 1 vCPU/1-2GB Droplet runs $6-12/month -- but it still needs someone to patch it, back it up and watch it, which RAD's managed Cloud SQL, Secret Manager and monitoring cover for you) is the cheaper-again option in cash terms, since this module's own footprint is small -- but you are back to patching and backing it up yourself.
- Either way, this is a team's workflow-automation backbone, so the running cost above is what actually drives the bill, not the module fee -- and that running cost is the one you can pause (see below).
Pause it for free: delete a RAD-managed project, restore it when you need it
This is the headline for a RAD-managed project. Deleting a RAD-managed project first unlinks its billing, then asks Google to delete the project outright -- Google's own 30-day recoverable soft delete. Unlike deleting one module, this does not tear down Cloud SQL, any VM or the compute resource one by one: the whole project simply stops, and nothing is charged while it waits, because billing is already unlinked.
Restoring, within 30 days and only by the project's owner, asks Google to undelete the project and reattaches its billing account, then asks you to run Update on each deployment to confirm everything came back. Because nothing was individually destroyed, that Update finds the same resources already there -- it is a check, not a rebuild, and an Update never charges the module fee again. This costs only a handful of credits (under US$1) in total for a typical 2-3-deployment chain.
What this needs: you must own the project (not one RAD only manages billing for), you must restore it yourself within 30 days -- after that Google deletes it for good -- and restoring is admitted like creating a new project, so your purchased credit balance must still clear the tier's floor (100 credits for the sandbox tier most study/demo use fits). Google says most services are fully working again within 36 hours of a restore.
One real gap: nightly backups are written to a bucket inside the project, and that bucket has Cloud Storage's soft-delete explicitly turned off, so it is very likely gone as soon as you delete the project -- even though the project itself is recoverable for 30 days. If you have customised the app and want to keep that work, copy a backup out (to Google Drive, or a bucket outside the project) before deleting. For a default install with nothing irreplaceable in it, this does not matter.
Pay only while you use it, the other way: delete and redeploy
In your own project (or once you are past the 30-day restore window above), the alternative is to delete N8N outright and redeploy it later. A redeploy costs the module fee again, plus the builds -- roughly 110 + 3-6 credits of build time.
Deleting saves money only once N8N would otherwise sit unused long enough to clear that redeploy cost against its own daily running cost -- against the own-project total above, that works out to about 3 days or more. Most of the running cost here is usually the database and the shared file/cache VM; they stop only when nothing else in the project uses them, so deleting this app while something else shares the project saves only this app's own compute part.
Keep data first: nightly backups go to a bucket inside the deployment and are deleted with it, so copy the latest backup out before deleting if you want to keep it.
Lab sessions and Managed Environments
- Lab sessions, for training: a trainer runs a session for a class. Each participant gets the app in their own Google Cloud project for 15 minutes to 24 hours, within an allowance the trainer sets. Either the trainer funds every place, or each participant pays for their own. Everything is deleted when the session ends and unused credits go back to the trainer.
- Managed Environments, for consultancies: a partner runs the app for a client from a ring-fenced wallet it funds, and settles with the client directly. If the wallet runs low, billing pauses and the data is kept, so nobody receives an unexpected charge. At the end the partner hands the project over and the deployments become the client's own.
- Credits can be bought in more than 20 currencies, including XAF, XOF, NGN, GHS, KES and ZAR, by card, bank transfer or mobile money.
Sources (8 October 2026): Google Cloud Billing Catalog API list prices; radmodules.dev/pricing for RAD's own fees and daily-credit estimates; https://cloud.google.com/resource-manager/docs/delete-restore-projects for the pause/restore mechanics; https://n8n.io/pricing for the named competitor's price.
1. Overview
n8n runs as a Node.js container on Cloud Run v2. The deployment wires together a focused set of Google Cloud services:
| Capability | Google Cloud service | Notes |
|---|---|---|
| Compute | Cloud Run v2 | Node.js service, 1 vCPU / 1 GiB by default, always-on (instance-based billing, min_instance_count = 1) so cron/schedule triggers and queue execution fire without an inbound request |
| Database | Cloud SQL for PostgreSQL 15 | Required — n8n uses PostgreSQL for all workflow and credential data |
| Shared files | Filestore (NFS) | Binary file data shared across all instances; also serves as the default Redis endpoint |
| Object storage | Cloud Storage | A dedicated data bucket |
| Queue & coordination | Redis | Enabled by default; enables n8n queue mode for horizontal scaling |
| Secrets | Secret Manager | Auto-generated encryption key and SMTP password placeholder |
| Ingress | Cloud Run URL / Cloud Load Balancing | Default run.app URL, optional external HTTPS load balancer + custom domain |
Sensible defaults worth knowing up front:
- PostgreSQL 15 is mandatory. The database engine is fixed; selecting any other
engine or
NONEbreaks startup. - Redis is enabled by default. Queue mode allows multiple n8n instances to distribute workflow execution. Without Redis, only one instance can run reliably.
- The encryption key is irreplaceable.
N8N_ENCRYPTION_KEYis generated once and stored in Secret Manager. All workflow credentials are encrypted with it. If the key is rotated or deleted, every saved credential becomes permanently unreadable. min_instance_countdefaults to1. n8n keeps one instance warm so webhooks and the scheduler/queue trigger without cold-start delay. Set it to0only if occasional webhook latency on cold start is acceptable.WEBHOOK_URLandN8N_EDITOR_BASE_URLare pre-set to the predicted Cloud Run service URL so webhooks resolve correctly from first start. If a custom domain is added later, redeploy to update these values.- Gen2 execution environment is required for NFS mounts.
execution_environmentdefaults to"gen2". - The SMTP password secret is seeded with a dummy value; update it in Secret Manager before configuring email sending.
2. Google Cloud Services & How to Explore Them
All commands assume PROJECT and REGION are set. Service and resource names are
reported in the deployment Outputs.
A. Cloud Run — the n8n service
n8n runs as a Cloud Run v2 service that autoscales by request load between the minimum and maximum instance counts. Each deployment creates an immutable revision; traffic can be split across revisions for safe rollouts.
- Console: Cloud Run → select the service for revisions, traffic, logs, and metrics.
- CLI:
gcloud run services list --project "$PROJECT" --region "$REGION"
gcloud run services describe <service-name> --project "$PROJECT" --region "$REGION"
gcloud run revisions list --service <service-name> --project "$PROJECT" --region "$REGION"
See App_CloudRun for scaling, concurrency, execution environment, and traffic splitting.
B. Cloud SQL for PostgreSQL 15
n8n stores all workflow definitions, execution history, and encrypted credentials
in a managed Cloud SQL for PostgreSQL 15 instance. The service connects privately
through the Cloud SQL Auth Proxy over a Unix socket (no public IP). The
entrypoint.sh script translates the platform-injected DB_* variables to
n8n-native DB_POSTGRESDB_* variables at runtime. On first deploy an
initialization Job creates the application database and user.
- Console: SQL → select the instance for connections, backups, flags, metrics.
- CLI:
gcloud sql instances list --project "$PROJECT"
gcloud sql instances describe <instance-name> --project "$PROJECT"
gcloud sql connect <instance-name> --user=<db-user> --project "$PROJECT"
The instance name, database, user, and password secret are in the Outputs. See App_CloudRun for the connection model, backups, and password rotation.
C. Filestore (NFS) and Cloud Storage
Binary files uploaded to or produced by workflows are written to a Filestore
(NFS) share mounted into the service so all instances share the same data
(N8N_DEFAULT_BINARY_DATA_MODE=filesystem). The NFS host IP also serves as the
default Redis endpoint when no explicit redis_host is configured. A dedicated
Cloud Storage bucket is provisioned for broader data persistence.
- Console: Filestore → Instances; Cloud Storage → Buckets.
- CLI:
gcloud filestore instances list --project "$PROJECT"
gcloud storage buckets list --project "$PROJECT"
gcloud storage ls gs://<data-bucket>/        # bucket name is in the Outputs
See App_CloudRun for the NFS mount, GCS Fuse, and CMEK.
D. Redis queue
Redis enables n8n's queue mode, distributing workflow executions across multiple instances using Bull. In queue mode one or more "worker" instances pick up executions from the queue while the main instance handles the editor and webhook registration. When no external Redis host is configured and NFS is enabled, the NFS host IP is used as the Redis endpoint.
- Console: Memorystore → Redis (if using a managed instance).
- CLI:
redis-cli -h <redis-host> ping
redis-cli -h <redis-host> info keyspace
E. Secret Manager
The n8n encryption key and the SMTP password placeholder are stored in Secret Manager and injected into the service at runtime.
- Console: Security → Secret Manager.
- CLI:
gcloud secrets list --project "$PROJECT"
gcloud secrets versions access latest --secret=<secret-name> --project "$PROJECT"
# Update the SMTP password with the real credential:
echo -n "my-real-smtp-password" | \
  gcloud secrets versions add <smtp-secret-name> --data-file=- --project "$PROJECT"
See App_CloudRun for injection and rotation details.
F. Networking & ingress
The service is reachable at its run.app URL by default. An external HTTPS load
balancer with a custom domain, Cloud CDN, and Cloud Armor can be layered on; ingress
settings and VPC egress control connectivity.
- Console: Cloud Run (service URL); Network services → Load balancing.
- CLI:
gcloud run services describe <service-name> --region "$REGION" --format='value(status.url)'
gcloud compute addresses list --project "$PROJECT"
See App_CloudRun.
G. Cloud Logging & Monitoring
Container logs flow to Cloud Logging; Cloud Run and Cloud SQL metrics flow to Cloud Monitoring, with optional uptime checks and alert policies.
- Console: Logging → Logs Explorer; Monitoring → Dashboards / Alerting.
- CLI:
gcloud run services logs read <service-name> --project "$PROJECT" --region "$REGION" --limit 50
3. n8n Application Behaviour
- First-deploy database setup. An initialization Job (
db-init) usespostgres:15-alpineto create the n8n database and user before the service starts. It is idempotent. - Environment variable translation.
entrypoint.shmapsDB_HOST,DB_NAME,DB_USER, andDB_PASSWORD(injected by the platform) to the n8n-nativeDB_POSTGRESDB_*equivalents at container startup. - Queue mode operation. With
enable_redis = true(the default), n8n starts in queue mode. The main instance handles webhook registration, the editor UI, and execution coordination; additional instances act as workers. - Webhook URL stability.
WEBHOOK_URLandN8N_EDITOR_BASE_URLare set to the predicted Cloud Run service URL before deployment. Adding a custom domain later requires a redeploy to update these values. - Scale-to-zero and webhooks.
min_instance_countdefaults to1, keeping an instance warm for webhook workloads. Setting it to0means no instance is running when idle — external services calling webhooks will experience cold-start latency and timeouts if the calling service has a short timeout. - Binary data storage.
N8N_DEFAULT_BINARY_DATA_MODE=filesystemdirects n8n to write binary files to the NFS-mounted filesystem rather than the database, which is required for multi-instance deployments. - Health path. Startup and liveness probes target the n8n root (
/), which returns HTTP 200 only once the application is fully initialised. The startup probe uses a 120-second initial delay for first-boot setup. - Encryption key criticality.
N8N_ENCRYPTION_KEYencrypts all workflow credentials. If it changes, all saved credentials become permanently unreadable.
4. Configuration Variables
Variables are grouped exactly as they appear on the deployment platform. Only settings specific to or notable for n8n are listed; every other input is inherited from App_CloudRun with its standard behaviour.
Group 1 — Project & Identity
| Variable | Default | Description |
|---|---|---|
project_id | (required) | Target Google Cloud project. |
region | us-central1 | Region for the service and regional resources. |
tenant_id | demo | Short suffix that makes resource names unique per environment. |
support_users | [] | Emails granted project access and monitoring alerts. |
resource_labels | {} | Labels applied to all resources. |
Group 3 — Application Identity
| Variable | Default | Description |
|---|---|---|
application_name | n8n | Base name for resources. Do not change after first deploy. |
display_name | N8N Workflow Automation | Friendly name shown in the Console. |
description | (set) | Cloud Run service description. |
application_version | 2.4.7 | n8n image version tag. |
Group 4 — Runtime & Scaling
| Variable | Default | Description |
|---|---|---|
deploy_application | true | Set false to provision infrastructure only without deploying the container. |
cpu_limit | 1000m | CPU per instance. |
memory_limit | 1Gi | Memory per instance. |
min_instance_count | 1 | Minimum instances. Keeps an instance warm for webhook workloads by default; set 0 to scale to zero. |
cpu_always_allocated | true | CPU allocated at all times (instance-based billing) — n8n's cron/schedule triggers and queue execution fire without an inbound request. |
max_instance_count | 1 | Maximum instances (cost ceiling). |
container_port | 5678 | n8n listens on port 5678. |
execution_environment | gen2 | Cloud Run execution generation. Gen2 required for NFS mounts. |
timeout_seconds | 300 | Max request duration in seconds. |
enable_cloudsql_volume | true | Cloud SQL Auth Proxy for socket connections. |
enable_image_mirroring | true | Mirror the n8n image into Artifact Registry. |
traffic_split | [] | Split traffic across revisions for staged rollouts. |
max_revisions_to_retain | 7 | Number of old Cloud Run revisions to keep. |
Group 5 — Access & Ingress Control
| Variable | Default | Description |
|---|---|---|
ingress_settings | all | Which networks may reach the service (all / internal / internal-and-cloud-load-balancing). |
vpc_egress_setting | PRIVATE_RANGES_ONLY | How outbound traffic is routed through the VPC connector. |
enable_iap | false | Require Google sign-in via Identity-Aware Proxy. |
iap_authorized_users / iap_authorized_groups | [] | Who may access through IAP. |
Group 6 — Environment Variables & Secrets
| Variable | Default | Description |
|---|---|---|
environment_variables | SMTP placeholder defaults | Extra non-secret settings. Core N8N_* and DB_TYPE values are set automatically. The default map includes SMTP_HOST, SMTP_PORT, SMTP_USER, SMTP_PASSWORD, SMTP_SSL, and EMAIL_FROM ready to override. |
secret_environment_variables | {} | Map of env var → Secret Manager secret name. |
secret_propagation_delay / secret_rotation_period | (set) | Replication wait / rotation cadence. |
Group 7 — Backup & Restore
| Variable | Default | Description |
|---|---|---|
backup_schedule | 0 2 * * * | Automated backup cron (UTC). |
backup_retention_days | 7 | Retention; raise for production/compliance. |
enable_backup_import / backup_source / backup_uri / backup_format | restore options | Restore from a backup on deploy. |
Group 8 — CI/CD & Binary Authorization
Standard App_CloudRun Cloud Build / Cloud Deploy integration — see
App_CloudRun. Key inputs: enable_cicd_trigger,
github_repository_url, github_token, enable_cloud_deploy,
enable_binary_authorization.
Group 9 — Custom SQL
| Variable | Default | Description |
|---|---|---|
enable_custom_sql_scripts / custom_sql_scripts_bucket / custom_sql_scripts_path / custom_sql_scripts_use_root | off | Run SQL from a GCS bucket after provisioning. |
Group 10 — Domain, CDN, Cloud Armor & Image Retention
| Variable | Default | Description |
|---|---|---|
application_domains | [] | Custom hostnames for the external load balancer. |
enable_cdn | false | Enable Cloud CDN on the LB backend. |
enable_cloud_armor / admin_ip_ranges | off | Attach a WAF policy / restrict privileged access. |
max_images_to_retain / delete_untagged_images / image_retention_days | (set) | Artifact Registry cleanup policy. |
Group 11 — Storage & Filesystem
| Variable | Default | Description |
|---|---|---|
enable_nfs | true | Shared Filestore volume for binary file data. Requires gen2. |
nfs_mount_path | /mnt/nfs | Mount path inside the container. |
nfs_instance_name / nfs_instance_base_name | (set) | Existing NFS instance / base name for an inline one. |
create_cloud_storage / storage_buckets / gcs_volumes | (set) | Data bucket / additional buckets / GCS Fuse mounts. |
manage_storage_kms_iam / enable_artifact_registry_cmek | false | CMEK options. |
Group 12 — Database Backend
| Variable | Default | Description |
|---|---|---|
database_type | POSTGRES_15 | Fixed — do not change. |
db_name | n8n_db | PostgreSQL database name. Immutable after first deploy. |
db_user | n8n_user | Application user. Immutable after first deploy. |
database_password_length | 32 | Generated password length (16–64). |
enable_auto_password_rotation / rotation_propagation_delay_sec | off | DB password rotation. |
db_host_env_var_name / db_name_env_var_name / db_user_env_var_name / db_port_env_var_name / service_url_env_var_name | (set) | Names under which connection details are injected. |
Group 13 — Jobs & Scheduled Tasks
| Variable | Default | Description |
|---|---|---|
initialization_jobs | [] | Leave empty to use the built-in db-init database setup job. |
cron_jobs | [] | Recurring jobs triggered by Cloud Scheduler. n8n's built-in scheduler handles workflow triggers; use these for external operations. |
Group 14 — Observability & Health
| Variable | Default | Description |
|---|---|---|
startup_probe / startup_probe_config | HTTP GET /, 120s initial delay | Startup probe targets the n8n root. |
liveness_probe / health_check_config | HTTP GET /, 30s initial delay | Liveness probe. |
uptime_check_config | { enabled=false, path="/" } | Optional Cloud Monitoring uptime check. |
alert_policies | [] | Metric alert policies. |
Group 21 — Redis Queue
| Variable | Default | Description |
|---|---|---|
enable_redis | true | Use Redis for queue-mode workflow execution. |
redis_host | "" | Redis endpoint. Leave empty to use the NFS host IP. |
redis_port | 6379 | Redis port. |
redis_auth | "" | Optional Redis auth password (sensitive). |
Group 22 — VPC Service Controls & Audit Logging
| Variable | Default | Description |
|---|---|---|
enable_vpc_sc | false | Enforce a VPC-SC perimeter (requires organization_id). |
vpc_cidr_ranges / vpc_sc_dry_run | (set) | Access level CIDRs / dry-run mode. |
enable_audit_logging | false | Detailed Cloud Audit Logs. |
5. Outputs
Returned on a successful deployment — the quickest way to locate and explore the running resources.
| Output | Description |
|---|---|
service_name | Cloud Run service name. |
service_url | Default run.app URL of the service. |
service_location | Region the service runs in. |
stage_services | Stage-specific service URLs (Cloud Deploy). |
load_balancer_ip / load_balancer_url | External HTTPS load balancer IP / URL (when enabled). |
database_instance_name | Cloud SQL instance name. |
database_name / database_user | Application database name / user. |
database_password_secret | Secret Manager secret holding the DB password. |
database_host / database_port | DB endpoint / port. |
storage_buckets | Created Cloud Storage buckets. |
network_name / network_exists / regions | VPC network, presence, regions. |
container_image / container_registry | Deployed image and Artifact Registry repo. |
monitoring_enabled / monitoring_notification_channels / uptime_check_names | Monitoring status, channels, uptime checks. |
initialization_jobs | Names of the setup jobs. |
deployment_id / tenant_id / resource_prefix | Naming identifiers. |
project_id / project_number | Project identifiers. |
cicd_enabled / github_repository_url / github_repository_owner / github_repository_name / cicd_configuration | CI/CD status and details. |
artifact_registry_repository / cloudbuild_trigger_name / cloudbuild_trigger_id | Registry and build trigger. |
vpc_sc_enabled / vpc_sc_perimeter_name / vpc_sc_dry_run_mode | VPC-SC status. |
audit_logging_enabled / artifact_registry_cmek_enabled | Audit logging and CMEK status. |
6. Configuration Pitfalls & Sensible Defaults
Risk: Critical (data loss / outage / security) — High (service degraded) — Medium (cost or partial degradation) — Low (minor).
| Setting | Sensible value | Risk | Consequence if wrong |
|---|---|---|---|
N8N_ENCRYPTION_KEY | (auto-generated, never rotate) | Critical | Rotating or deleting this key destroys all saved workflow credentials permanently. |
db_name / db_user | set once | Critical | Immutable after first deploy; renaming recreates the DB/user and destroys all workflow data. |
enable_nfs | true | Critical | Without shared storage, binary files are not shared across instances and filesystem binary mode fails. |
enable_backup_import | false unless restoring | Critical | Enabling without a valid backup_uri fails the import job. |
enable_redis | true | High | Without Redis queue mode, running more than one instance causes workflow execution conflicts. |
redis_host | "" (NFS) or explicit | High | No valid endpoint if Redis is on but NFS is off and no host is set. |
min_instance_count | 1 (default) for webhook workloads | High | Setting 0 causes cold-start timeouts on webhook calls from services with short timeouts. |
execution_environment | gen2 (default) | High | NFS mounts require Gen2; Gen1 instances cannot mount NFS volumes. |
memory_limit | 4Gi | High | Too little memory causes OOM during large workflow execution batches. |
enable_iap / enable_cloud_armor | enable for production | Medium | The n8n editor is otherwise publicly reachable and exposes all saved credentials. |
backup_retention_days | 7 (raise for prod) | Medium | Too short for compliance retention. |
For the foundation behaviour referenced throughout — service identity, scaling and concurrency, ingress and load balancing, CI/CD, Cloud Armor, IAP, Binary Authorization, VPC-SC, backups, and image mirroring — see App_CloudRun. n8n-specific application configuration shared with the GKE variant is described in N8N_Common.
Related guides
- Hands-on lab: N8N on Cloud Run — deploy it step by step, with the console screens and commands at each stage.
- n8n on GKE Autopilot — the same application on Kubernetes, for when you need the other deployment target.
- N8N Common — Shared Application Configuration — the configuration shared by both deployment targets.
- Deployed alongside Mautic on Google Cloud Run, Listmonk on Google Cloud Run, Matomo on Google Cloud Run, Shlink on Google Cloud Run in the Marketing Automation Suite solution.
Need RAD to do something it does not do yet? Request it on the roadmap, or vote on what is already there.